What crypto custody means
Crypto custody is the safeguarding or administration of digital assets, or control over the means that can transfer them, for a client. A custody arrangement may involve the firm operating wallets, a specialist custodian holding keys, or a hybrid setup in which several parties perform different steps. The important question is not simply where a token appears on a blockchain. It is who has the legal or contractual entitlement, who can initiate or approve a transfer, and what records demonstrate the arrangement.
For a digital asset business, custody connects technology, operations, legal terms, finance, compliance and customer communication. A secure wallet can still sit inside a weak custody model if client entitlements are unclear, access is poorly governed, records are incomplete or a third party can act without effective oversight.
The EU’s Markets in Crypto-Assets Regulation (MiCA), Article 75, requires providers of custody and administration services to establish a custody policy and describes duties including a client position register, client agreements, asset return and liability for loss attributable to an incident. The exact legal analysis depends on the service and the rules in force. In the UK, the FCA’s new cryptoasset regime and CASS 17 safeguarding rules are scheduled to take effect on 25 October 2027; as at 7 October 2026, firms should distinguish preparation for that regime from current obligations. See the MiCA text and the FCA regime overview.
Map the custody arrangement before choosing controls

Start with a service map. Identify each point where a client asset, entitlement or transfer instruction is created, recorded, controlled or passed to another party. Include onboarding terms, wallet creation, deposit attribution, internal ledger updates, withdrawal requests, approvals, blockchain broadcast, reconciliation, incident handling and termination.
Then document the operating model. A useful map identifies:
- The contracting entity and the client-facing service.
- The entity that holds or controls each key or signing component.
- The wallets, networks and asset types in scope.
- Whether assets are held in an individual or pooled address structure.
- Which records establish the client’s entitlement and how often they are updated.
- The third parties that can affect access, availability or transaction execution.
- What happens when a transfer is delayed, reversed by an internal process, or sent to the wrong address.
Terms such as “self-custody”, “non-custodial” or “segregated” should match the real allocation of control. If a provider has a means to bring about a transfer, or can alter a client’s access to assets, the firm should assess the legal and regulatory classification with qualified advisers. The FCA’s perimeter guidance discusses how control may affect whether a service is safeguarding; it is not enough to rely on a product label.
Build a client asset protection framework

Client asset protection begins with a clear account of rights and responsibilities. The customer agreement should explain the service, the firm’s role, the treatment of assets, use of sub-custodians where relevant, and the process for withdrawals and service termination. Legal wording should be consistent with the actual wallet and ledger design.
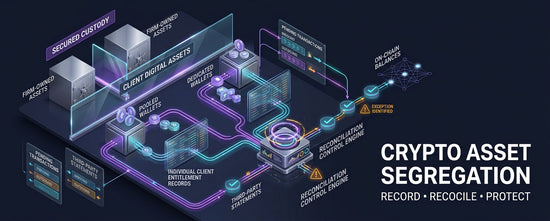
At the control level, separate client assets from the firm’s own assets in records and operational processes. Depending on the business model and applicable law, this may include wallet separation, tagged addresses, sub-ledgers, trust arrangements or other safeguards. A technical separation alone does not establish the legal character of an asset; conversely, a contractual promise without reliable operational records can be difficult to evidence.
Define responsibilities across custody operations, finance, compliance, technology and senior management. Name control owners, deputies, escalation routes and decision rights. Establish approval thresholds for unusual transfers, wallet changes, emergency access and exceptions. Keep a record of the decision, supporting evidence and post-event review.
Govern wallets and control access
Wallet architecture should reflect the asset, transaction volume, availability needs and risk appetite. Hot wallets can support timely withdrawals but remain connected to online systems. Cold or offline storage can reduce some exposure while creating recovery, availability and process risks. A blended model may be suitable, provided movements between wallet tiers are controlled and monitored.
Private-key management should address creation, storage, backup, access, rotation or migration, recovery and destruction. Map each key share or signing authority to a person, device, service and business purpose. Use least-privilege access, strong authentication, separation of duties and independent approval for sensitive operations. Multi-signature or threshold-signing arrangements can distribute authority, but they do not remove the need for identity checks, secure devices, clear procedures and tested recovery. 
Withdrawal controls should verify that the request is authorised, complete, within limits and consistent with the customer’s account status and applicable risk checks. High-risk changes—such as a new destination address, a change to wallet policy, or an emergency key recovery—should have a defined verification path. Keep an immutable or protected audit trail showing request, approvers, system actions, transaction identifier and outcome.
Keep records and reconcile positions

A custody ledger should allow the firm to answer, for each client and asset: what is owed, what is held or controlled, where it is held, and what movements remain pending. Records should distinguish client balances from firm-owned assets and avoid treating an unconfirmed blockchain transaction as final without a defined policy.
Reconciliation compares records that serve different purposes. For example, a firm may compare its client sub-ledger, wallet or custodian statements, and on-chain balances. Define timing, asset units, confirmation rules, fee treatment, pending transactions and exception ownership. A reconciliation is only useful if someone investigates differences, records a resolution and escalates aged or material breaks.
The FCA’s published CASS 17 materials for the future UK regime include requirements concerning records and reconciliations. They are useful for readiness planning, but their future effective date matters. Under MiCA Article 75, custody providers must maintain a position register and regularly provide a statement of positions. Firms should verify the precise requirements applicable to their service and jurisdiction rather than generalising a single rule globally.
Manage third parties and operational incidents
A custodian, cloud provider, wallet technology vendor or blockchain infrastructure provider can affect client asset access. Due diligence should cover service scope, legal entity, control environment, key access, subcontractors, incident notification, business continuity, audit rights, data portability, exit support and financial or operational dependencies. Reassess the provider when its service, ownership, control model or material subcontractors change.
Outsourcing a control does not remove the need for internal accountability. Assign a business owner, define service measures, obtain incident and control evidence, and maintain a realistic exit plan. Consider concentration risk: several services may depend on the same cloud region, key-management platform or individual administrator.
Incident playbooks should cover suspected key compromise, unauthorised transfer, chain or protocol outage, custodian unavailability, inaccurate balance records and suspected insider activity. The playbook should state who may pause withdrawals, isolate systems, notify clients or regulators, and authorise recovery. Preserve logs and transaction evidence while limiting unnecessary access to sensitive information.
Prepare for disruption and insolvency
Resilience planning asks whether the firm can continue critical custody functions—or stop them safely—when systems or people fail. Test backups, recovery credentials, alternative approvers, communications channels and the ability to reconstruct client positions from independent records. An untested backup may be incomplete, inaccessible or dependent on the same compromised credentials as the primary environment.
Insolvency readiness requires more than an emergency contact list. The firm should be able to identify assets, client entitlements, legal arrangements, pending transactions, third-party dependencies and the steps needed to return or transfer assets under the relevant legal process. Maintain records in formats that can be accessed if the usual platform is unavailable. Ensure the wind-down plan identifies who can access the information and what authority they need.
This is a planning discipline, not a promise that every client will receive immediate or complete recovery in every failure scenario. Ownership, segregation, insolvency law, asset shortfalls and chain-level events can affect outcomes. Obtain legal advice for the firm’s structure and jurisdictions.
A practical custody control checklist
- Map the service, entities, asset flows and parties with transfer power.
- Align customer terms, wallet architecture and ledger treatment.
- Maintain an asset and wallet inventory with named owners.
- Apply least privilege, dual control and monitored emergency access.
- Verify withdrawal requests and independently approve sensitive changes.
- Reconcile client records to wallet, custodian and on-chain data on a risk-based schedule.
- Assign and age reconciliation breaks; retain evidence of resolution.
- Assess third parties and concentration risks; test exit arrangements.
- Exercise incident, recovery and wind-down plans.
- Review jurisdictional requirements and document the applicable rule version.
Frequently asked questions
Is crypto custody just the storage of private keys?
No. Key security is central, but custody also includes control rights, client entitlements, records, approvals, reconciliations, third-party oversight and the ability to return assets.
Does a separate wallet prove that client assets are legally segregated?
Not by itself. Wallet separation can support operational control, but legal segregation depends on applicable law, contractual arrangements and how the firm actually holds and records assets.
How often should a crypto custodian reconcile assets?
There is no universal interval for every service. Set frequency using asset risk, transaction volume, system design, applicable rules and the time in which a break could cause harm. Document exceptions and escalation thresholds.
What is the difference between a custody policy and a wallet procedure?
A custody policy explains the firm’s overall safeguarding approach, responsibilities and control principles. Wallet procedures describe how staff and systems carry out specific tasks such as key access, approvals, transfers and recovery.
What does MiCA say about custody?
MiCA Article 75 sets requirements for crypto-asset service providers providing custody and administration on behalf of clients. These include a custody policy, client position records, client agreements and rules relating to return and liability. Read the regulation and obtain advice on its application.
Is the UK CASS 17 crypto safeguarding regime already in force?
The FCA states that the new UK cryptoasset regime is expected to commence on 25 October 2027. As of 7 October 2026, CASS 17 is future-dated; firms can prepare, while separately checking obligations already applicable to their activities.
Build your custody knowledge
Professionals who need a structured grounding in wallet governance, private-key management, segregation, reconciliation, resilience and insolvency preparedness can review the Crypto Custody, Safeguarding and Client Asset Protection Controls course. The six-hour, self-paced course is designed for compliance, custody, risk, operations, legal and audit professionals.