Crypto-asset businesses operating in the European Union face a more established regulatory environment in 2026. For crypto-asset service providers (CASPs), obtaining authorization is only one part of meeting the requirements of the Markets in Crypto-Assets Regulation (MiCA).
MiCA compliance for CASPs means meeting the EU's requirements for authorization, governance, prudential safeguards, client asset protection, business conduct, and ongoing regulatory oversight. The specific obligations depend on the services a provider offers and its regulatory status.
The regulation's transitional arrangements reached their EU-wide endpoint on July 1, 2026. This makes it especially important for businesses to understand whether they are authorized to provide crypto-asset services and whether their operating arrangements meet the applicable requirements.
This guide explains MiCA compliance requirements in 2026, including authorization, capital, governance, safeguarding, and practical implementation. It also considers how the rules may affect Australian and other international crypto businesses entering the EU market.
What Is MiCA Compliance for CASPs?
MiCA is the European Union's regulatory framework for specified crypto-assets and related services. Established under Regulation (EU) 2023/1114, it introduces harmonized requirements intended to support market integrity, consumer protection, and regulatory consistency across the EU.
The regulation also includes MiCA white paper requirements for relevant crypto-asset offers and admissions to trading, which are distinct from the general CASP authorization framework.
For CASPs, compliance involves more than meeting the conditions for initial authorization. Providers must also maintain appropriate arrangements for managing risks, protecting clients, and conducting regulated activities.
What Is a Crypto-Asset Service Provider?
A crypto-asset service provider is a legal person or other undertaking whose occupation or business involves providing one or more regulated crypto-asset services to clients on a professional basis.
Under MiCA, these services can include operating trading platforms, exchanging crypto-assets, safeguarding client crypto-assets, executing orders, and providing crypto-asset advice.
The classification depends on the activities performed, rather than the business's preferred description.
For example, a company describing itself as a technology platform may still provide regulated crypto-asset services if its actual activities fall within MiCA's definitions.
What Does MiCA Compliance Require?
A CASP's obligations generally involve several connected areas:
- Authorization: Obtaining the appropriate permission or satisfying an applicable regulatory notification route.
- Governance: Maintaining suitable management arrangements, responsibilities, policies, and internal controls.
- Prudential safeguards: Meeting financial safeguard requirements applicable to the services provided.
- Client protection: Safeguarding client assets, managing conflicts, and providing appropriate information.
- Operational compliance: Maintaining procedures, records, oversight, and controls appropriate to the business.
MiCA establishes common requirements, but not every CASP is subject to identical obligations. A trading platform, custodial wallet provider, and crypto-asset adviser may face different service-specific rules.
Understanding those differences is the starting point for effective compliance.
Who Must Comply With MiCA?
MiCA applies to businesses providing crypto-asset services within its regulatory scope in the EU.
Whether a business requires authorization depends on the services it provides, the crypto-assets involved, its activities within the EU, and whether another applicable regulatory route or exclusion applies.
Businesses uncertain about their regulatory status should first understand who needs a MiCA licence and which activities qualify as regulated crypto-asset services.
Which Crypto-Asset Services Fall Under MiCA?
MiCA identifies ten categories of crypto-asset services.
|
Regulated service |
Example of the activity |
|
Custody and administration |
Safeguarding crypto-assets or controlling access to them on behalf of clients |
|
Operating a trading platform |
Bringing together third-party buying and selling interests in crypto-assets |
|
Exchange for funds |
Exchanging crypto-assets for money |
|
Exchange for other crypto-assets |
Exchanging one crypto-asset for another |
|
Execution of orders |
Concluding agreements to buy or sell crypto-assets on behalf of clients |
|
Placing of crypto-assets |
Marketing crypto-assets to purchasers on behalf of an offeror or related party |
|
Reception and transmission of orders |
Receiving client orders and transmitting them for execution |
|
Advice on crypto-assets |
Providing personalized recommendations concerning crypto-assets or related services |
|
Portfolio management |
Managing portfolios containing crypto-assets under a client mandate |
|
Transfer services |
Transferring crypto-assets on behalf of clients between addresses or accounts |

These definitions are important because the applicable authorization, capital, conduct, and operating requirements depend partly on the services involved.
A company offering several services must evaluate its obligations across those activities rather than assuming that compliance with one service category is sufficient.
Does MiCA Apply to Non-EU Crypto Businesses?
MiCA can be relevant to businesses established outside the EU when they seek to provide regulated crypto-asset services to clients within the Union.
A company cannot assume that remaining incorporated outside Europe removes the need to assess EU requirements.
However, having an EU customer does not automatically establish that every service or interaction requires CASP authorization. The regulatory analysis must consider how the service is offered, whether the provider actively targets EU clients, and whether a relevant exclusion or exemption applies.
MiCA includes a limited provision concerning services initiated at the exclusive initiative of a client. This is commonly associated with reverse solicitation.
It should not be treated as a general alternative to authorization. Marketing activities, solicitation, and efforts to expand services beyond a genuinely client-initiated request can affect whether the provision applies.
Are Non-Custodial Wallets and DeFi Services Covered?
Non-custodial wallets and decentralised finance (DeFi) arrangements require careful analysis to determine whether MiCA applies.
- Non-custodial wallets: Providing software that allows users to control their own private keys does not necessarily constitute a regulated custody service. However, a business may still provide another regulated crypto-asset service.
- Fully decentralised services: MiCA recognises that crypto-asset services provided in a fully decentralised manner without an intermediary may fall outside its scope.
- Decentralisation is not an automatic exemption: A product's decentralised features alone do not establish that it is exempt from MiCA.
- Assessing the operating model: Businesses should examine who operates the service, who exercises control and which activities are actually performed.
The key consideration is whether the operating model involves a regulated intermediary or service, rather than simply whether the product is described as decentralised.
MiCA Deadlines and CASP Requirements in 2026
MiCA became applicable in stages, allowing businesses and regulators time to prepare for the new framework.
For CASPs, the major implementation dates are now in the past.
When Did MiCA Start Applying to CASPs?
|
Date |
Regulatory development |
|
June 29, 2023 |
MiCA entered into force |
|
June 30, 2024 |
Provisions concerning asset-referenced tokens and e-money tokens began applying |
|
December 30, 2024 |
The main CASP provisions and most remaining MiCA requirements began applying |
|
July 1, 2026 |
The maximum EU-wide transitional period for qualifying existing CASPs ended |

The earlier introduction of MiCA stablecoin rules established requirements for asset-referenced tokens and e-money tokens, with implications for how certain tokens can be offered and supported in the EU market.
Article 143 permitted certain providers already operating lawfully under applicable national rules before December 30, 2024, to continue temporarily under specified conditions.
Member States could shorten that period or decline to apply it.
Consequently, some national transitional arrangements ended before July 2026.
What Happens After the MiCA Transitional Period?
The July 1, 2026 deadline marked the end of the EU-wide MiCA transitional period, changing the position for providers that previously relied on transitional arrangements.
In its April 2026 supervisory statement, ESMA confirmed that unauthorized CASPs could not continue providing regulated services to EU clients merely by relying on the expired transitional regime.
ESMA also emphasized orderly wind-down arrangements and client protection for businesses unable to obtain the required authorization.
A CASP should therefore establish its current legal basis for operating, rather than relying on historical national registration alone.
Understanding MiCA vs VASP registration helps businesses distinguish the previous national registration arrangements from the authorization framework now applicable under MiCA.
Businesses planning to enter the EU market must also understand that the expiry of the transitional period does not eliminate the need to follow the appropriate authorization process.
MiCA Authorization Requirements for CASPs
Authorization determines whether a provider may lawfully conduct particular regulated crypto-asset services within the applicable MiCA framework.
The requirements are designed to assess whether a business has the organization, resources, governance, and operating arrangements needed to provide those services.
For a more detailed explanation of licensing routes and regulatory expectations, see our guide to MiCA CASP authorisation.
CASP Authorization and Article 60 Notification
MiCA provides different regulatory routes depending on the type and existing status of the business.
Article 59 establishes the general framework under which crypto-asset services may be provided by appropriately authorized CASPs or eligible entities operating in accordance with Article 60.
Article 60 allows certain existing regulated financial entities to provide specified crypto-asset services through a notification procedure, subject to the conditions applicable to their category.
These routes are not interchangeable.
|
Article 59 authorization |
Article 60 notification |
|
General authorization route for businesses seeking CASP status |
Available to specified categories of existing regulated financial entities |
|
Requires assessment by the relevant competent authority |
Requires the prescribed notification information and compliance with applicable conditions |
|
Covers the services included within the authorization |
Permitted services depend on the institution's category and relevant MiCA provisions |
|
Subject to applicable ongoing MiCA requirements |
Does not automatically exempt the institution from all relevant service obligations |
A firm should establish which route is available before preparing an application or planning its operating structure.
What Information Is Needed for a MiCA Application?
Article 62 identifies information required for a CASP authorization application.
Depending on the business and services proposed, the application covers areas such as:
- Business activities: The services to be provided, business model, operating arrangements, and program of operations.
- Governance: Management arrangements, responsible individuals, organizational structure, and relevant suitability information.
- Financial safeguards: Evidence of compliance with applicable prudential requirements.
- Internal controls: Policies and procedures addressing relevant regulatory and operational responsibilities.
- Client protection: Safeguarding arrangements, complaints handling, and other relevant client-facing procedures.
- Service-specific information: Additional details concerning custody, trading, execution, advice, or other proposed activities.
Authorities assess the application against MiCA and applicable implementing requirements.
Submitting documentation does not itself mean authorization has been granted.
Can an Authorized CASP Operate Across the EU?
MiCA creates a framework for authorized CASPs to provide covered services across EU Member States.
This is commonly described as EU passporting.
The MiCA passporting rules explain how authorized CASPs can extend covered services across EU Member States through the applicable notification procedures.
Under the relevant notification arrangements, an authorized CASP may provide services in another Member State without obtaining an entirely separate CASP authorization in every country.
However, passporting does not remove the obligation to comply with applicable MiCA requirements or other relevant laws.
Businesses must also remain within the scope of the services they are permitted to provide.
Key MiCA Compliance Requirements for CASPs
Obtaining authorization is an important milestone, but CASPs must continue meeting applicable regulatory requirements throughout their operations.
MiCA addresses governance, financial safeguards, client protection, business conduct, and operational oversight. These areas work together to support a functioning compliance framework.
Governance and Management Responsibilities
Article 68 establishes governance requirements for CASPs.
Management bodies must have appropriate knowledge, skills, experience, and suitability to carry out their responsibilities.
CASPs must also establish suitable governance arrangements, including effective policies and procedures designed to support compliance and appropriate risk management.
In practice, this requires clarity about who is responsible for decisions, how important risks are identified, and how management receives information about compliance matters.
For example, a crypto exchange may establish defined responsibilities for monitoring customer complaints, reviewing operational incidents, and escalating significant concerns to senior management.
These arrangements should reflect the business's size, activities, and complexity.
Capital and Prudential Safeguards
MiCA Article 67 requires CASPs to maintain prudential safeguards at all times equal to at least the higher of:
- The applicable permanent minimum capital requirement under Annex IV.
- One-quarter of the previous year's fixed overheads, reviewed annually.
For CASPs that have been providing services for less than one year, the fixed-overheads calculation is based on the projected overheads for their first 12 months of service provision, as submitted with their authorization application.
The minimum capital thresholds depend on the types of crypto-asset services provided.
|
CASP Class |
Types of Services |
Minimum Capital Requirement |
|
Class 1 |
Order execution, placing crypto-assets, transfer services, reception and transmission of orders, advice, and portfolio management |
€50,000 |
|
Class 2 |
Class 1 services, plus custody and administration, and exchange of crypto-assets for funds or other crypto-assets |
€125,000 |
|
Class 3 |
Class 1 and Class 2 services, plus operating a crypto-asset trading platform |
€150,000 |
These thresholds represent minimum capital requirements, not necessarily the total prudential safeguards a CASP must maintain.
For a detailed breakdown of service classifications, own funds and prudential safeguards, see the MiCA capital requirements guide.
For example, a provider operating a crypto-asset trading platform falls within Class 3. However, its required safeguards may exceed €150,000 if one-quarter of its applicable fixed overheads produces a higher amount.
MiCA permits qualifying forms of prudential safeguards, subject to specific conditions. Businesses should therefore assess both the required amount and the permitted form of safeguards when evaluating compliance.
Client Asset Safeguarding and Custody
Protecting client assets is particularly important for CASPs that hold crypto-assets or funds on behalf of customers.
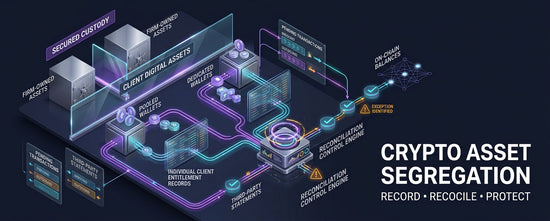
MiCA includes requirements concerning safekeeping arrangements, client rights, asset records, and the appropriate separation of client assets from a provider's own assets.
For businesses providing custody and administration, Article 75 establishes additional rules addressing matters such as custody agreements, position registers, and the safekeeping of client crypto-assets.
The operational arrangements must reflect the actual service.
For example, a custodial wallet provider may need procedures for recording client entitlements, managing access to private keys, and responding to incidents affecting client assets.
Safeguarding should not be treated solely as a cybersecurity task. It also involves governance, legal responsibilities, accurate records, and operational controls.
Conduct of Business and Customer Protection
Article 66 requires CASPs to act honestly, fairly, and professionally in accordance with clients' best interests.
This principle is supported by more specific obligations concerning client communications and business conduct.
Relevant requirements include clear information, fair treatment, conflicts-of-interest management, and complaints handling.
A business should ensure its client-facing procedures reflect the services it provides.
For example, customer support personnel should understand how to identify complaints, direct them through the appropriate process, and avoid making misleading statements about regulatory protections.
The objective is to make fair treatment and regulatory compliance part of ordinary business operations.
Outsourcing and Operational Controls
Many crypto businesses rely on external technology providers, custody solutions, infrastructure operators, and other service partners.
MiCA Article 73 addresses outsourcing arrangements for CASPs.
Outsourcing must not undermine a provider's responsibility for meeting its obligations or prevent effective supervisory oversight.
A CASP should understand which activities depend on external providers and how related risks are managed.
This may involve appropriate contractual arrangements, monitoring, access to information, and contingency planning.
A critical point is that outsourcing an activity does not mean outsourcing regulatory accountability.
|
Compliance area |
Practical operational focus |
|
Governance |
Defined responsibilities and management oversight |
|
Prudential safeguards |
Monitoring required financial resources |
|
Safeguarding |
Client asset protection and accurate records |
|
Business conduct |
Fair communications, complaints, and conflicts |
|
Outsourcing |
Supplier oversight and retained accountability |

The effectiveness of these arrangements depends on whether they operate consistently, not simply whether policies exist.
Additional MiCA Rules for Specific Crypto Services
MiCA combines general obligations applicable to CASPs with additional rules for particular services.
A provider offering multiple regulated activities may therefore need controls addressing several different sets of requirements.
Trading Platforms, Exchange, and Order Execution
Trading platforms must consider service-specific requirements concerning operating rules, fair and orderly trading, and relevant market transparency.
Businesses should also understand the applicable MiCA market abuse rules, including obligations concerning the prevention and detection of market abuse in crypto-assets.
Providers exchanging crypto-assets for funds or other crypto-assets face requirements relating to the services they offer, including applicable pricing and commercial arrangements.
Execution services also involve obligations concerning how client orders are handled.
For instance, a business operating a trading platform needs to consider the integrity and operation of the platform itself, while a provider executing client orders must evaluate the requirements applicable to execution practices.
These differences make accurate service classification essential.
Crypto Custody, Advice, and Portfolio Management
Custodial services involve obligations concerning the safekeeping and administration of client crypto-assets.
Providers giving advice on crypto-assets or managing portfolios face additional client protection requirements.
Under Article 81, relevant obligations include assessing suitability and taking account of information about clients where the regulation requires it.
Consequently, an advisory business cannot assume that the compliance arrangements suitable for a basic crypto exchange will also satisfy its responsibilities.
CASPs should review the service-specific provisions that correspond to every regulated activity they provide.
How MiCA Relates to AML, the Travel Rule, and DORA
MiCA is an important part of the EU crypto regulatory environment, but it is not the only framework relevant to CASPs.
Other legislation establishes requirements concerning financial crime, information accompanying transfers, and digital operational resilience.
Understanding the relationship between these rules helps prevent compliance gaps and unnecessary duplication.
MiCA and AML/CFT Obligations
Anti-money laundering and counter-terrorist financing (AML/CFT) obligations fall under the applicable EU AML/CFT framework and relevant national requirements. These obligations are separate from MiCA authorisation and conduct requirements, although a business may need to comply with both.
For a more detailed explanation of MiCA AML/CTF obligations, including how separate EU financial crime requirements affect CASPs, see our supporting guide.
Key financial crime responsibilities may include:
- Customer due diligence: Verifying customers and understanding relevant risks.
- Risk assessment: Identifying and assessing potential money laundering and terrorist financing risks.
- Transaction monitoring: Monitoring transactions for suspicious activity.
- Suspicious activity reporting: Reporting suspicious activity in accordance with applicable requirements.
- Recordkeeping: Maintaining required records to support compliance and regulatory oversight.
CASPs should identify the rules applicable to their activities and integrate appropriate financial crime controls into their broader compliance arrangements.
MiCA and the Crypto Travel Rule
The EU Transfer of Funds Regulation establishes requirements concerning information accompanying certain transfers of funds and crypto-assets.
For relevant crypto-asset transfers, CASPs may need to obtain, verify, retain, or transmit specified information about originators and beneficiaries, depending on the applicable provisions.
The Travel Rule is not simply another name for MiCA. It is a separate legislative framework that interacts with CASP operations.
Businesses should evaluate both sets of requirements when designing transfer procedures.
MiCA and Digital Operational Resilience
The Digital Operational Resilience Act (DORA) establishes digital operational resilience requirements for financial entities within its scope, including relevant CASPs.
DORA addresses areas such as ICT risk management, operational incidents, resilience testing, and third-party ICT risk.
For a CASP, cybersecurity arrangements must therefore be considered alongside applicable resilience and governance obligations.
A sound compliance framework should recognize the different purposes of MiCA, AML/CFT legislation, the Transfer of Funds Regulation, and DORA rather than treating them as a single legal requirement.
A closer comparison of MiCA vs DORA helps CASPs understand how crypto-asset obligations differ from ICT risk and operational resilience requirements.
Does MiCA Apply to Australian Crypto Businesses?
Australian crypto businesses may encounter MiCA when expanding internationally, particularly when seeking to provide regulated crypto-asset services in the EU.
However, Australian and EU regulatory obligations must be considered separately.
When Might an Australian CASP Need MiCA Authorization?
An Australian crypto business operating only in Australia does not automatically require MiCA authorization.
The position changes when the business proposes to provide services that fall within MiCA's scope in the EU.
For example, an Australian exchange planning to offer custody and exchange services to EU clients must assess whether its proposed activities require authorization under the EU framework.
Its Australian incorporation does not itself provide an exemption.
The business should consider the services offered, intended EU market activity, relevant legal entity arrangements, and any available regulatory route.
MiCA Authorization vs Australian Crypto Regulation
Australia regulates digital asset activities through its own legal framework, which operates separately from the EU's MiCA regime.
The Australian Securities and Investments Commission (ASIC) explains how Australian financial services laws apply to digital assets through its digital assets guidance.
Whether a business requires an Australian financial services licence or another applicable authorization depends on the nature of its digital assets, the rights and arrangements involved, and the activities it performs. Not every crypto business is subject to identical licensing requirements.
AUSTRAC oversees anti-money laundering and counter-terrorist financing obligations, including registration requirements for businesses providing designated virtual asset services.
Australia's 2026 AML/CTF reforms expanded regulation to additional virtual asset services. Certain newly regulated services received transitional arrangements, including a July 29, 2026 registration application deadline for qualifying existing providers. Businesses should consult AUSTRAC registration requirements to understand the conditions relevant to their activities.
|
Regulatory Issue |
European Union |
Australia |
|
Main crypto service framework |
MiCA |
Applicable Australian financial services and digital asset laws |
|
Relevant authorities |
National competent authorities, with ESMA and EBA performing designated roles |
ASIC and AUSTRAC, according to their respective responsibilities |
|
Authorization or registration |
MiCA CASP authorization or another applicable route |
Licensing depends on the asset and activity, while AUSTRAC registration applies to designated virtual asset services |
|
AML/CTF obligations |
Applicable EU and national AML/CFT requirements |
Australian AML/CTF framework |
|
Cross-border recognition |
MiCA provides an EU passporting framework |
Australian registration does not itself grant a MiCA passport |
The two frameworks serve different jurisdictions and should not be treated as interchangeable. Australian crypto businesses planning to provide regulated services in the EU must assess MiCA requirements separately from their domestic obligations.
Practical Example: An Australian Exchange Entering the EU
Consider an Australian cryptocurrency exchange that is registered with AUSTRAC and plans to expand into the EU.
The company proposes to provide crypto-to-fiat exchange services and custodial wallet facilities to customers in several EU countries.
Before launch, it would need to assess whether those activities fall within MiCA's regulated service categories and determine the appropriate authorization arrangements.
It would also need to review governance, prudential safeguards, custody, customer protection, and related requirements relevant to its proposed services.
Meanwhile, the company would continue assessing its obligations under Australian law.
Its AUSTRAC registration would not replace MiCA authorization.
This example demonstrates why cross-border compliance planning must account for both the services being provided and the jurisdictions involved.
How CASPs Can Build and Maintain MiCA Compliance
MiCA compliance is more effective when regulatory requirements are translated into clear responsibilities and operational processes.
A business may possess detailed policies yet still encounter problems if employees do not understand their responsibilities or management lacks reliable information about whether controls are working.
The following four-stage framework provides a practical approach to organizing compliance. It is an implementation model, not a regulator-prescribed sequence.
1. Identify Applicable Obligations and Assess Gaps
Start by identifying the crypto-asset services the business provides and matching them to relevant MiCA requirements.
The assessment should consider current authorization status, governance, financial safeguards, client protection, service-specific obligations, and related regulatory frameworks.
Compare those requirements with existing processes and documentation.
For example, a custodial provider may identify that it has technical wallet security procedures but needs stronger governance documentation or evidence of how client asset records are reviewed.
A gap assessment should distinguish between missing arrangements, ineffective controls, and documentation that no longer reflects actual practices.
2. Assign Compliance Responsibilities
Effective compliance requires clear accountability.
Senior management should understand the regulatory responsibilities associated with the business and receive appropriate information about material risks.
Compliance and risk personnel may coordinate assessments, monitoring, reporting, and regulatory change management.
Operational teams are responsible for following applicable procedures within their roles.
The exact arrangements will depend on the organization's structure, size, services, and regulatory obligations.
Documenting responsibilities helps reduce uncertainty when a problem arises or a procedure needs review.
3. Implement Policies, Procedures, and Operational Controls
After identifying gaps, the business should establish or update the required controls.
These may relate to client asset safeguarding, complaints, conflicts of interest, outsourcing, financial safeguards, recordkeeping, and operational oversight.
Policies should explain responsibilities and expectations. Procedures should explain how those expectations are carried out.
For example, a complaints procedure might identify how complaints are received, recorded, investigated, escalated, and resolved.
It should also make clear which employees are responsible for each stage.
Controls must reflect how the business actually operates rather than relying on generic templates.
4. Monitor Compliance and Review Control Effectiveness
Compliance arrangements need ongoing attention.
Monitoring helps management understand whether procedures are followed and whether emerging risks require action.
Useful activities may include internal reviews, management reporting, analysis of complaints, incident follow-up, and review of outsourced services.
Where deficiencies are identified, the business should document appropriate remedial action and review whether improvements have been effective.
Regulatory changes should also be monitored so that outdated policies do not remain in use.
The aim is to maintain a functioning compliance system that supports everyday decisions and can provide appropriate evidence of how obligations are met.

Why MiCA Compliance Training Matters for CASPs
Even well-designed compliance procedures depend on the people responsible for implementing them.
CASP employees may work with regulated services, customer information, crypto-asset transfers, complaints, internal controls, and sensitive operational systems.
Understanding the responsibilities associated with those activities helps reduce mistakes and supports consistent implementation.
Which CASP Employees Need Compliance Knowledge?
Training needs should reflect the responsibilities of different roles.
For example:
- Senior management needs an understanding of governance, accountability, regulatory expectations, and material compliance risks.
- Compliance and risk professionals require more detailed knowledge of applicable obligations, controls, monitoring, and regulatory developments.
- Operations personnel need to understand the procedures governing the services they perform.
- Customer-facing employees should recognize relevant disclosure, complaint-handling, and escalation responsibilities.
- Technology and security personnel may need role-specific knowledge of safeguarding, incident handling, and operational resilience requirements.
The appropriate depth of training will vary.
MiCA contains specific competence and knowledge expectations in relevant areas, including provisions concerning management and crypto-asset advice. However, it should not be interpreted as requiring every CASP employee to complete the same commercial training course.
How Training Supports Ongoing MiCA Compliance
Training helps translate regulatory expectations into practical understanding.
Employees who understand their responsibilities are better placed to follow internal procedures, recognize unusual situations, escalate concerns, and maintain accurate records.
For example, customer service personnel may need to distinguish a routine question from a formal complaint requiring specific handling.
Similarly, operational teams working with client crypto-assets should understand the controls relevant to their responsibilities.
Training is most useful when it reflects actual roles and is supported by appropriate internal procedures and supervision.
Global Compliance's MiCA Compliance for Crypto-Asset Service Providers (CASPs) course is a relevant learning option for businesses and professionals seeking to strengthen their understanding of the regulatory framework.
Training should complement, rather than replace, suitable governance arrangements, legal assessment, and operational controls.
Common MiCA Compliance Challenges and How to Address Them
Implementing MiCA requirements can involve significant coordination between regulatory, operational, financial, and technical functions.
The challenges vary according to the services offered and the maturity of existing controls.
|
Common challenge |
Practical response |
|
Incorrect service classification |
Review actual activities against MiCA service definitions |
|
Confusion about authorization status |
Confirm the applicable legal route and authorization details |
|
Incomplete governance documentation |
Align policies and responsibilities with operational practices |
|
Client asset recordkeeping weaknesses |
Review safeguarding procedures, records, and reconciliation controls |
|
Dependence on external providers |
Evaluate outsourcing arrangements and monitoring responsibilities |
|
Changes in regulatory expectations |
Maintain a process for reviewing relevant regulatory developments |
|
Inconsistent employee understanding |
Provide role-appropriate information and training |
One recurring difficulty is assuming that obtaining authorization resolves every regulatory issue.
In reality, compliance continues as the business changes.
A CASP may introduce a new service, expand its customer base, change infrastructure providers, or enter another market. Each development can affect the requirements that need to be considered.
Regular review allows the compliance framework to evolve alongside the business.
How to Check Whether a CASP Is MiCA-Authorized
Businesses and customers can use official regulatory information to check whether a provider appears to hold the relevant MiCA authorization.
ESMA provides access to its MiCA register, which includes regulatory information concerning authorized CASPs and other relevant records.
When checking a provider:
- Identify the legal entity behind the service, not only its trading name.
- Search for the entity in the relevant regulatory information.
- Check its authorization status and recorded crypto-asset services.
- Compare those details with the activities the provider claims to offer.
- Review any relevant information from the national competent authority.
Regulatory records should be interpreted carefully, including their update dates and scope.
Authorization is an important regulatory consideration, but it does not guarantee that a crypto-asset investment is safe or that a business cannot experience financial or operational difficulties.
Conclusion
MiCA compliance for CASPs is an ongoing responsibility that extends beyond obtaining authorization.
Businesses must understand which services fall within the regulation, establish the appropriate legal basis for providing those services, and maintain the governance, prudential safeguards, client protection measures, and operational arrangements relevant to their activities.
The end of the EU-wide transitional period in July 2026 has made current authorization status particularly important.
For international businesses, including Australian crypto providers considering EU expansion, compliance planning also requires a clear distinction between EU requirements and domestic regulatory obligations.
A practical starting point is to review the services offered, confirm the applicable regulatory requirements, assess existing controls, and identify areas requiring improvement.
With clear responsibilities, effective procedures, and appropriate staff knowledge, CASPs can approach MiCA compliance as an integral part of responsible business operations.
Frequently Asked Questions
Does MiCA Apply to Crypto Companies Outside the EU?
MiCA can apply to non-EU businesses when their activities involve providing regulated crypto-asset services within its scope in the EU. Whether authorization is required depends on the services, market activity, and relevant legal circumstances. Operating from outside the EU does not automatically provide an exemption.
Can a CASP Operate in the EU With Only VASP Registration?
Legacy national VASP registration does not automatically replace MiCA authorization. The EU-wide transitional period ended on July 1, 2026. Businesses must establish that they have the appropriate authorization or another applicable legal basis, such as a qualifying Article 60 route, before providing regulated services.
Is MiCA Authorization Valid Across the EU?
MiCA provides an EU passporting framework for authorized CASPs. Subject to the applicable notification procedures and regulatory requirements, authorized providers can offer covered services across Member States without obtaining a separate CASP authorization in every country. The provider must remain within the scope of its permitted activities.
Does MiCA Regulate Non-Custodial Wallet Providers?
Not every non-custodial wallet provider is automatically regulated as a CASP. The position depends on the activities performed, the provider's role, and whether those activities fall within MiCA's definitions. Providing software alone may differ from operating a regulated service involving client crypto-assets.
Is MiCA Compliance the Same as AML Compliance?
No. MiCA primarily establishes regulatory requirements for specified crypto-assets and crypto-asset services. AML/CFT obligations arise under separate applicable legislation. CASPs may need to comply with both frameworks, as well as the Transfer of Funds Regulation and other relevant requirements.
Do Australian Crypto Businesses Need MiCA Authorization?
Australian businesses do not automatically require MiCA authorization merely because they operate in Australia. However, they may need to meet MiCA requirements when providing regulated crypto-asset services in the EU. Australian registration or licensing does not itself provide authorization under the EU framework.